Introduction
Modern enterprise applications rarely consist of a single backend service. Instead, they are built using microservices, cloud-native platforms, AI services, and distributed systems that must communicate efficiently and securely. As applications become more complex, managing communication between clients and backend services becomes increasingly challenging.
An API Gateway solves this challenge by acting as the single entry point for all client requests. According to Google Cloud, an API gateway works as a reverse proxy that accepts API requests, routes them to appropriate backend services, aggregates responses when necessary, and returns the final result to clients. It also centralizes authentication, authorization, traffic management, monitoring, and security policies.
The growing importance of API gateways is reflected in the market itself. The global API gateway market was valued at approximately $1.18 billion in 2024 and is projected to reach nearly $4.47 billion by 2031, driven primarily by microservices adoption and enterprise API management.
An API Gateway is far more than a reverse proxy. It acts as the central management layer that secures, routes, monitors, and optimizes communication between clients and distributed backend services.
What Is an API Gateway?
An API Gateway is a server positioned between clients and backend services that provides a unified interface for accessing multiple APIs or microservices. Instead of clients communicating with numerous backend services individually, every request passes through the gateway first.
The gateway determines where requests should be routed while handling cross-cutting concerns such as authentication, authorization, request validation, caching, load balancing, and monitoring. Backend services remain focused solely on business logic while the gateway manages infrastructure-related responsibilities.
This centralized architecture simplifies client applications, strengthens security, improves observability, and reduces network complexity across enterprise environments.
Key Responsibilities of an API Gateway
| Responsibility | Description |
|---|---|
| Request Routing | Directs incoming requests to the correct backend service. |
| Authentication | Verifies user or application identity before allowing access. |
| Authorization | Enforces permissions based on user roles and access policies. |
| Rate Limiting | Prevents API abuse and protects backend services from overload. |
| Load Balancing | Distributes requests across multiple service instances. |
| Caching | Stores frequently requested responses to improve performance. |
| SSL Termination | Handles HTTPS encryption and reduces backend processing overhead. |
| Logging & Monitoring | Collects metrics, logs, and performance data for observability. |
| Request Validation | Validates request structure, headers, and payload before forwarding. |
Modern API Gateway Architecture
In a modern enterprise environment, every request flows through the API gateway before reaching backend services. The gateway centralizes authentication, routing, monitoring, caching, and security while backend services remain dedicated to business functionality.
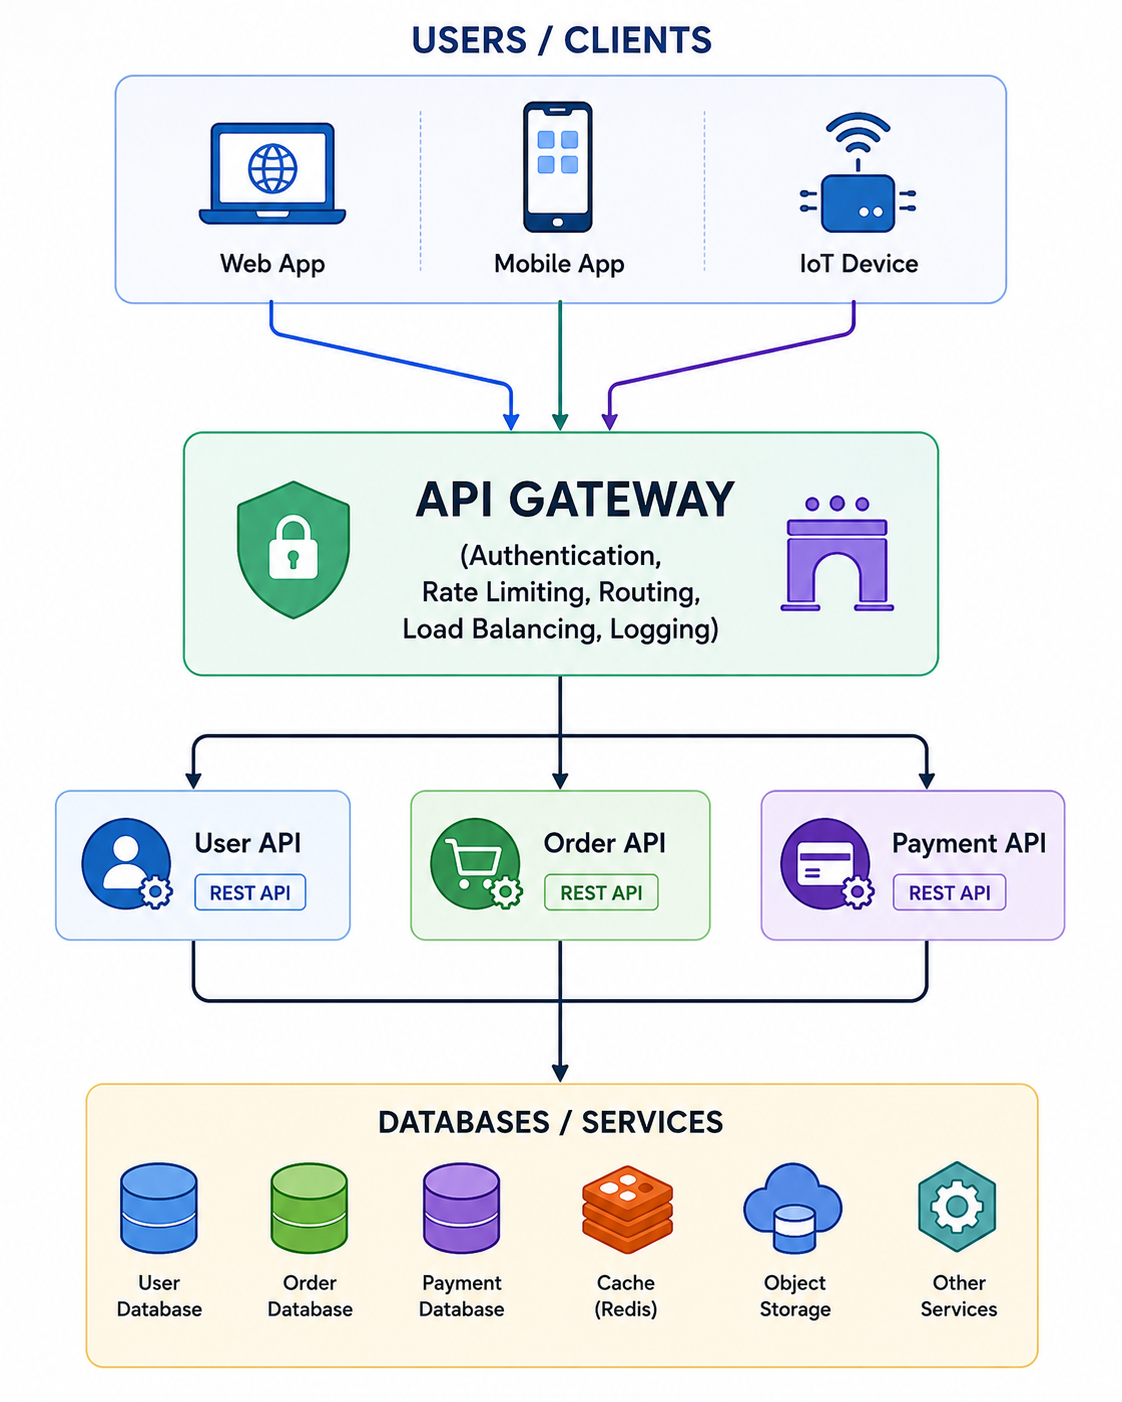
API Gateway with Microservices Architecture
Microservices architecture often consists of dozens of independent services. Rather than exposing every service directly, the API gateway provides a unified interface for clients while internally routing requests to the appropriate microservice and combining responses whenever multiple services are involved.
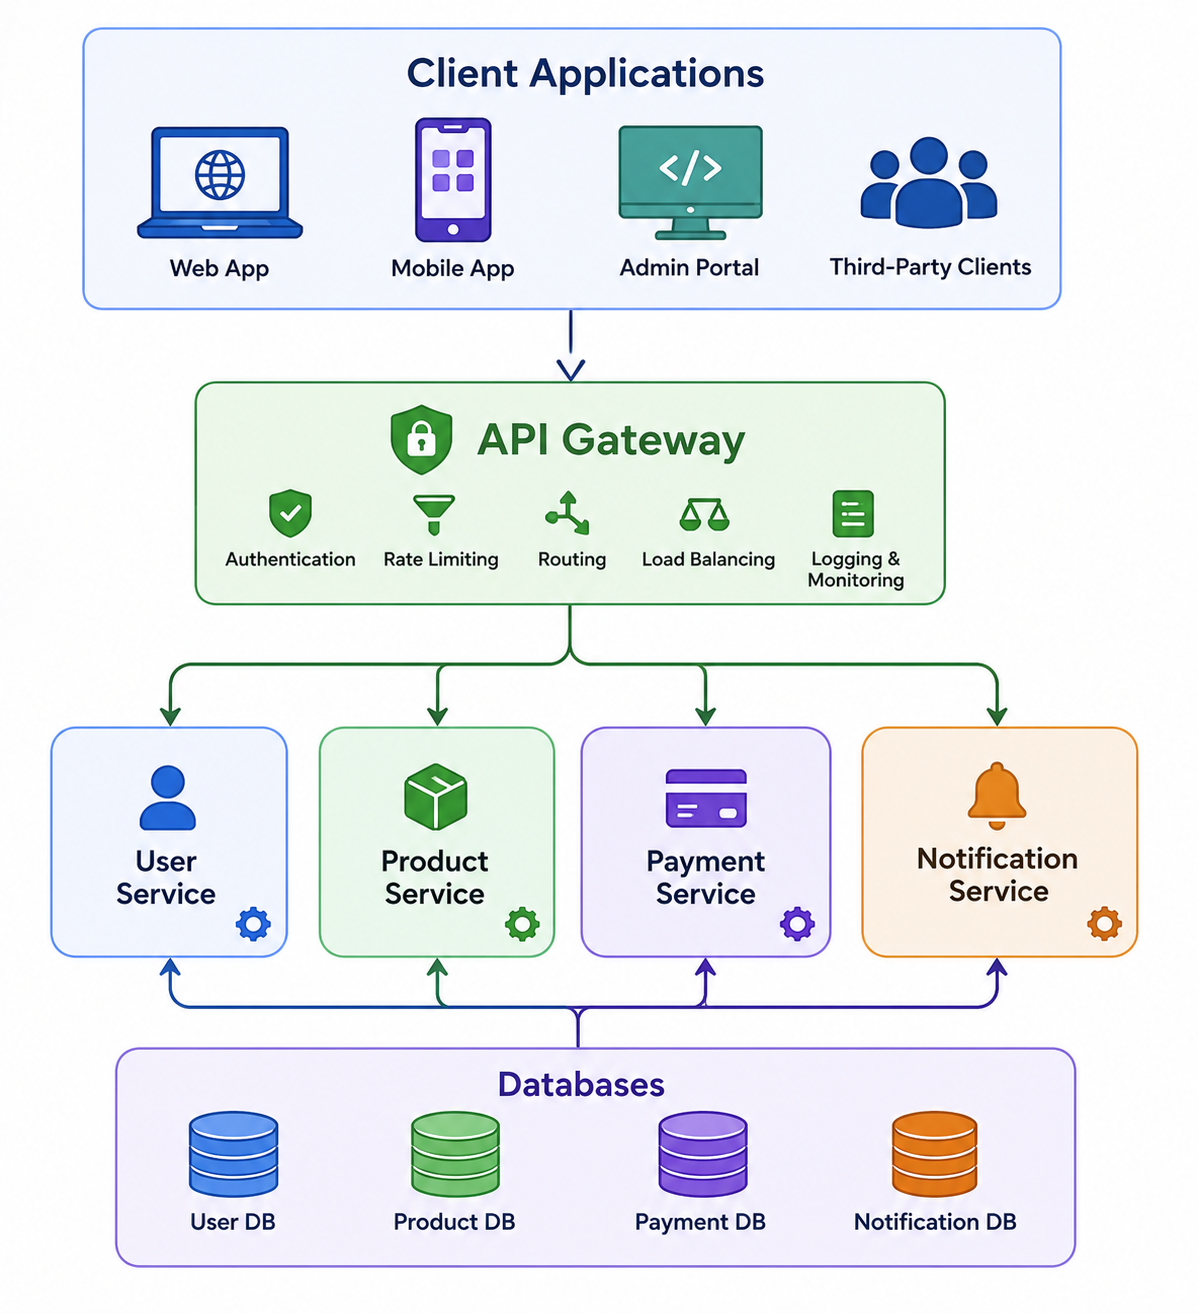
How an API Gateway Works
Every client request follows a structured lifecycle before reaching backend services. The API gateway validates the request, applies security policies, determines where the request should be routed, and finally forwards it to the appropriate microservice. This centralized workflow ensures that backend services remain secure, scalable, and focused solely on business logic.
The gateway first authenticates the client using mechanisms such as OAuth 2.0, JWT tokens, or API keys. It then verifies authorization policies, applies rate limiting to protect backend services, validates incoming requests, and routes them to the appropriate microservice. After processing, the response is returned to the client through the gateway.
Core Components of an API Gateway
Authentication and Authorization
Authentication verifies the identity of the client before granting access, while authorization determines what resources the authenticated client is allowed to access. Modern API gateways support API Keys, JWT, OAuth 2.0, OpenID Connect, and enterprise Identity and Access Management (IAM) systems.
Rate Limiting
Rate limiting prevents excessive API requests from overwhelming backend services. Organizations typically configure limits based on users, IP addresses, API keys, or subscription plans to ensure fair resource utilization and protection against denial-of-service attacks.
Request Routing
The gateway intelligently routes requests to backend services using URL paths, request headers, HTTP methods, query parameters, or custom routing rules. This abstraction allows backend services to evolve without impacting client applications.
Load Balancing
Incoming traffic is distributed across multiple service instances, improving availability, fault tolerance, and application performance. Load balancing also enables horizontal scaling during peak traffic periods.
Caching
Frequently requested responses can be cached at the gateway layer, reducing backend workload and significantly lowering response latency for clients.
SSL Termination
API gateways handle SSL/TLS encryption and decryption, allowing backend services to focus on application logic while maintaining secure client communication.
Logging and Monitoring
Comprehensive logging and monitoring provide insights into API traffic, request latency, error rates, and system health. These metrics help organizations optimize performance and quickly diagnose operational issues.
Types of API Gateways
| Gateway Type | Purpose |
|---|---|
| Enterprise API Gateways | Comprehensive API management, governance, analytics, monetization, and developer portals. |
| Microservices Ingress Gateways | Routing, SSL termination, authentication, and load balancing for Kubernetes environments. |
| Unified Gateway Platforms | Combine API gateway management with Kubernetes ingress capabilities. |
Security remains one of the primary reasons organizations deploy API gateways. Every incoming request passes through multiple layers of protection including Web Application Firewalls (WAF), authentication, authorization, rate limiting, and threat detection before reaching backend services. This centralized security model significantly reduces organizational risk while improving compliance.
API Gateway Design Patterns
API gateway design patterns help organizations build scalable, secure, and maintainable distributed systems. Instead of placing business logic inside the gateway, these patterns focus on handling cross-cutting concerns such as routing, authentication, traffic management, and request aggregation while allowing backend services to remain independent.
Pattern 1: Gateway Aggregation
Gateway aggregation combines responses from multiple backend services into a single response before sending it back to the client. Rather than making separate requests to product, inventory, pricing, and review services, the client makes one request to the API gateway, which gathers all required information and returns a unified response.
Pattern 2: Gateway Offloading
Instead of implementing authentication, SSL termination, logging, and rate limiting inside every microservice, these common responsibilities are handled centrally by the API gateway. This simplifies backend services and improves maintainability.
Pattern 3: Gateway Routing
The gateway intelligently routes requests based on URL paths, request headers, HTTP methods, or custom routing rules. This enables canary deployments, blue-green deployments, API versioning, and A/B testing without changing client applications.
Pattern 4: Edge Gateway
An edge gateway acts as the first point of contact between external users and enterprise services. It is commonly deployed at the network edge or within Content Delivery Networks (CDNs) to reduce latency while enforcing security policies before requests enter internal infrastructure.
API Gateway vs Load Balancer vs Reverse Proxy
| Aspect | Load Balancer | Reverse Proxy | API Gateway |
|---|---|---|---|
| Primary Purpose | Distribute Traffic | Proxy Requests | Manage APIs |
| Protocol | Layer 4 (TCP) | Layer 7 (HTTP) | Layer 7 (HTTP) |
| Authentication | Limited | Basic | Advanced |
| Rate Limiting | No | Limited | Yes |
| Analytics | No | No | Comprehensive |
Although these technologies share certain responsibilities, their objectives differ significantly. Load balancers primarily distribute traffic, reverse proxies forward requests between clients and servers, while API gateways provide complete API lifecycle management, including security, monitoring, analytics, routing, and traffic control.
API Gateway Deployment Considerations
Scaling API Gateways
Production API gateways are typically deployed using horizontal scaling. Container orchestration platforms like Kubernetes automatically increase or decrease gateway instances based on traffic, CPU utilization, or custom monitoring metrics to maintain consistent performance.
High Availability
Multiple gateway instances are deployed behind global load balancers to eliminate single points of failure. If one instance becomes unavailable, traffic is automatically redirected to healthy instances without affecting users.
Observability
Comprehensive monitoring includes centralized logging, distributed tracing, metrics collection, and real-time alerting. Integrating tools such as Prometheus, Fluentd, and Jaeger enables organizations to quickly detect bottlenecks and improve API performance.
Benefits of API Gateways
Implementing an API gateway provides organizations with a centralized layer for managing security, performance, traffic, and monitoring. Rather than configuring these capabilities within every individual microservice, enterprises can enforce consistent policies through a single gateway, simplifying operations and improving scalability.
| Benefit | Impact |
|---|---|
| Centralized Security | Single point for authentication, authorization, and threat detection. |
| Simplified Client Code | Clients communicate with one endpoint instead of multiple services. |
| Improved Performance | Caching, request aggregation, and optimized routing reduce latency. |
| Operational Observability | Unified monitoring, logging, and analytics across APIs. |
| Traffic Management | Rate limiting, load balancing, and circuit breaking improve reliability. |
| Developer Productivity | Simplifies API versioning, documentation, and service integration. |
| Cost Optimization | Efficient routing and caching reduce infrastructure costs. |
Popular API Gateway Technologies
| Technology | Type | Primary Use Case |
|---|---|---|
| AWS API Gateway | Cloud Managed | AWS-native applications |
| Google Cloud Apigee | Enterprise | Enterprise API management |
| Azure API Gateway | Cloud Managed | Azure-native applications |
| NGINX | Open Source / Enterprise | High-performance reverse proxy |
| Envoy | Open Source | Service mesh deployments |
| Kong | Open Source / Enterprise | API management on Kubernetes |
| Traefik | Open Source | Cloud-native ingress routing |
Challenges in API Gateway Design
| Challenge | Mitigation Strategy |
|---|---|
| Single Point of Failure | Deploy multiple gateway instances with load balancing. |
| Performance Overhead | Implement caching and optimize gateway resources. |
| Configuration Complexity | Use Infrastructure as Code and GitOps workflows. |
| API Versioning | Adopt path-based or header-based versioning. |
| Security & Compliance | Regular audits, IAM integration, and WAF deployment. |
| Vendor Lock-in | Prefer open standards and multi-cloud architectures. |
Best Practices
- Implement Zero-Trust Security
Authenticate every request, authorize every operation, and enforce rate limiting using OAuth 2.0 or OpenID Connect. - Use Declarative Configuration
Manage routes, policies, and gateway configuration as code for easier versioning and automated deployments. - Implement Circuit Breaking
Prevent failing services from affecting the entire application by temporarily stopping requests to unhealthy services. - Apply Caching Strategically
Cache frequently accessed responses while implementing proper cache invalidation policies. - Monitor Everything
Track latency, traffic, API usage, security events, and application health using centralized monitoring tools. - Design for Versioning
Plan API evolution early using consistent versioning strategies to avoid breaking existing clients. - Automate Deployment
Use CI/CD pipelines to validate and deploy gateway configurations safely across environments.
How MHTECHIN Supports API Gateway Implementation
Designing and deploying enterprise API gateways requires expertise across networking, security, cloud infrastructure, Kubernetes, and API management. MHTECHIN helps organizations implement secure, scalable, and production-ready gateway solutions that simplify API operations while strengthening security.
- API Gateway Architecture Design — Designing scalable and resilient gateway architectures.
- Authentication & Authorization — Implementing OAuth 2.0, JWT, API Keys, and OpenID Connect.
- API Analytics & Observability — Deploying centralized monitoring, logging, and analytics solutions.
- Training & Upskilling — Helping engineering teams adopt API gateway best practices and operational excellence.
By combining API engineering, cloud-native technologies, networking expertise, and security best practices, MHTECHIN enables organizations to build API gateway infrastructures that are secure, scalable, observable, and ready for enterprise workloads.
Future Trends in API Gateway Design
AI-Powered Gateways
Artificial Intelligence is transforming API management by enabling gateways to analyze traffic patterns, detect anomalies, predict failures, and automatically optimize routing decisions in real time.
Gateway as a Service
Managed API gateway platforms continue to gain popularity, reducing operational overhead while offering integrated monitoring, developer portals, and automated scaling capabilities.
eBPF and High Performance
Modern gateways increasingly leverage eBPF to improve observability and reduce networking overhead, resulting in lower latency and better runtime performance.
Standardized Kubernetes Gateway API
The Kubernetes Gateway API is emerging as the preferred standard for configuring ingress and API gateways, providing a unified and strongly typed configuration model for cloud-native environments.
Conclusion
API gateways have become an essential component of modern enterprise architectures by providing a centralized layer for authentication, routing, traffic management, observability, and security. As organizations continue adopting microservices, Kubernetes, and AI-powered applications, the importance of scalable and intelligent API management will continue to grow.
Emerging technologies such as AI-driven gateways, eBPF, Gateway as a Service, and the Kubernetes Gateway API are shaping the next generation of API management. Organizations that invest in modern gateway architectures today will be better positioned to build secure, resilient, and highly scalable digital platforms for the future.

Leave a Reply